AI glasses privacy begins with a question that ordinary eyewear never raised: what happens to the sights and sounds a device encounters while someone is wearing it? Camera-equipped glasses can photograph a street, interpret a sign, translate speech or help a user identify an object. Some of those functions depend on information about people nearby, even when those people have not chosen to interact with the device.
The hardware may look like conventional frames, but it combines cameras, microphones, wireless connections and computing systems. A voice command can start a chain of operations that extends from the glasses to a phone and, for certain requests, to remote servers. Other commands may run largely on the device. Understanding that distinction is more useful than assuming every AI feature is either entirely private or permanently recording.
Privacy involves three separate questions: what sensors collect, where their data is processed and what remains afterward. Recording indicators, encryption and account settings address parts of the problem. They cannot, by themselves, establish whether an unrelated person understood that a camera or microphone was being used.
The Hardware Behind AI Glasses
Wearable cameras in smart glasses typically place a small image sensor in the frame alongside several microphones near the temples. Speakers can deliver audio while leaving the ears relatively open. A processor handles sensor input, basic control functions and communication with a companion phone or network connection.
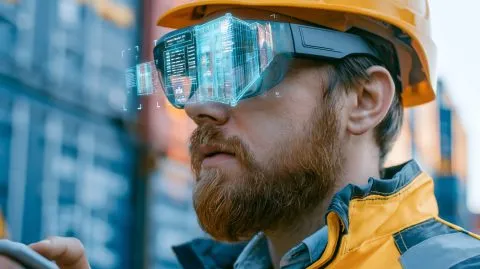
Hardware varies widely between products. Some glasses have no display and respond through audio. Others show notifications or visual prompts in a lens, sometimes using a paired wrist accessory for gesture input. A display adds another output option; it does not mean the device performs every AI calculation locally.
Battery capacity, heat, and frame weight constrain how much computing can run continuously. Designers must balance responsiveness against energy consumption, especially for camera analysis and speech processing. Those limits help explain why wearable AI often relies on both local software and remote services.
TechAmerica.ai has covered the distinction between conventional eyewear and smart glasses with displays and gesture controls. The underlying privacy questions apply to both display and displayless designs.
What Happens When a User Asks a Visual Question?
A wearer might ask an assistant to describe a sign or identify an unfamiliar object. The glasses first need an image or a selected set of frames. Software may crop, resize or otherwise prepare the visual input before an image-understanding system examines it.
Some recognition tasks can run on a specialized local processor. Smart glasses privacy depends in part on those processing choices. More demanding requests may require a cloud model because of memory or computing limits. The final response can return as synthesized speech or, on compatible glasses, as information displayed in the lens.
It is important to distinguish temporary visual input from a conventional photograph saved in a gallery. A product may handle an AI camera request without creating a user-accessible photo. That does not mean image data was never processed, transmitted or temporarily retained by the systems completing the request.
Actual behavior depends on the device, software version, feature and privacy settings. A reliable product explanation should identify the data path for each capability rather than making one sweeping promise about all camera activity.
Why a Recording Light Does Not Tell the Whole Story
Many camera glasses use an outward-facing light to indicate photo or video recording. Such a signal can help bystanders recognize that the wearer is creating shareable media. Some devices also try to prevent gallery recording when the indicator is blocked or altered.
However, the relationship between camera use and the light is not identical across functions or product generations. Some newer eyewear designs distinguish a camera view supplied to an AI feature from a photo or video being saved for the user’s gallery. Their recording indicator may therefore behave differently during AI analysis.
A dark indicator should not be treated as universal proof that no visual sensing is taking place. The relevant questions are what an indicator signifies, which activities activate it and whether the public can readily understand the distinction.
On October 13, 2026, the European Data Protection Board raised transparency concerns about smart glasses and recommended clear, reliable signals when people may be recorded. The statement highlights bystanders’ interests and the wearer’s choices.
How Voice Commands Are Detected and Processed
Hands-free operation often starts with a wake phrase or a physical control. Low-power audio processing can listen for the activation pattern without requiring a large cloud model to interpret every sound. What happens after activation depends on the request and the product’s architecture.
Speech recognition converts spoken language into text or another representation that software can use. A simple command, such as changing playback volume, may be handled locally. An open-ended question or live translation session may involve additional models and network processing.
Microphones also collect background noise. A bystander’s speech can become part of the voice data when the wearer asks for a summary or translation. Even if a system does not deliberately identify that person, the sound may contain personal information.
Voice activation is not infallible. An unintended trigger, misunderstood phrase, or poorly handled permission can cause an unexpected interaction. Good controls make it easy to stop listening, review voice-data settings and understand when remote processing begins.
On-Device AI and Cloud AI Have Different Privacy Trade-Offs
On-device processing keeps specified operations within the glasses or a paired device. It can reduce the amount of raw information sent across a network and may improve response time for narrow tasks. Smaller models, however, can struggle with complex questions or large amounts of context.
Cloud processing provides access to more computing capacity and potentially more capable models. It also means that some information leaves the immediate device environment. Encryption can protect data in transit, but it does not answer every question about processing access, retention or secondary use.
Developers may combine the two approaches, sending only selected inputs to a remote service after local filtering. That architecture can reduce exposure, although its effectiveness depends on what is filtered and whether the protections are independently tested.TechAmerica. AI’s reporting on compact models running on smart-glasses hardware illustrates why local AI is a relevant engineering direction. A demonstration of one model running locally does not establish that every commercial smart-glasses feature works offline.
Can Confidential Computing Protect Cloud Requests?
Some wearable-AI architectures use confidential computing to limit who can inspect information while it is processed on remote infrastructure. Trusted execution environments isolate workloads using hardware-backed protections. Remote attestation can help a device verify the software environment before sending sensitive information.
Other techniques separate a request from account identity through relays or privacy-preserving credentials. These measures may make it harder for an infrastructure operator to link a particular request to a user. They are technical safeguards, not a substitute for clear product documentation.
Guarantees depend on implementation details, the threat model and the software running inside the protected environment. A secure processing enclave cannot prevent a user from voluntarily sharing a result, nor can it automatically resolve concerns about a bystander’s image being captured in the first place.
An independent security review should examine the attestation process, permitted code, logging, and what happens when a device cannot verify a trusted environment. Product announcements alone do not establish that every request receives the same protection.
Where Photos, Transcripts and Interaction Records Can Remain
The privacy impact of a capture does not end when an assistant answers. A conventional photo might be stored on the glasses before being imported to a phone. A voice request may create a transcript, while an AI service may keep operational records under its applicable policies.
Those are different data categories with potentially different retention rules. Deleting an image from a phone does not necessarily erase a copy that was already shared elsewhere. Removing an account’s recording may also differ from removing information used during an earlier model-training process.
Users should look for data retention controls covering gallery imports, cloud history, voice recordings, backups and information used to improve services. Descriptions should explain whether a feature is off by default and how long its records can persist.
Organizations evaluating wearables need the same detail in contracts and technical documentation. Ambiguous claims that content is private or secure do not explain who can access it, under what conditions or for how long.
Why Bystanders Have Less Control Than Wearers
AI glasses privacy becomes a shared problem in public spaces. A wearer may be able to review permissions and delete files. Still, someone standing nearby cannot inspect the current mode or determine whether a camera frame is being analyzed remotely.
This imbalance matters in a classroom, medical facility, workplace or private conversation. A system designed around the purchaser’s consent may not adequately address the people whose voices or images also enter the device.
The EDPB’s 2026 statement identifies bystander transparency as a major problem and highlights the risks in sensitive environments. It encourages clearer recording signals and broader awareness of how the devices work.
Bystander privacy may benefit from visible indicators, restricted recording modes and data minimization. Behavioral rules matter too: ask permission, respect private spaces, and avoid capturing what would be inappropriate.
When European Data Protection Rules May Apply
European privacy requirements depend partly on a recording’s purpose and context. A private family recording is not necessarily governed in the same way as filming for a business, public account or organizational operation.
In its October 2026 statement, the European Data Protection Board explained that certain purely personal activities may fall within the GDPR’s household exemption. Public sharing and professional uses can create different responsibilities, including those of a data controller. Other civil, employment or criminal rules may still apply even when the GDPR does not.
Device manufacturers and app providers also have obligations when they determine the purposes and means of processing personal information. They cannot simply transfer every responsibility to the person wearing the glasses.
Readers should not interpret these general principles as legal permission to record anywhere. Local rules, venue policies and the people involved can change the analysis. Sensitive workplaces need specific legal and operational review.
Privacy Risks From Connected Apps and Developer Access
Smart glasses increasingly connect to phone applications, personal services and developer-built experiences. A useful app may request camera frames, microphone input or motion information. Each additional integration expands the range of software that could receive sensitive context.
Camera and microphone permissions should identify the requested capability and explain its purpose. Access can be limited by task or session where the platform supports that design. Broad permissions that remain available after a feature is no longer used create unnecessary exposure.
Developers should also inspect logs and diagnostic tools. A harmless-looking error report may include a transcript, image reference or location-related context. Test environments need synthetic data rather than uncontrolled recordings of customers or bystanders.
Connectivity and platform policies change over time, so device owners should review granted permissions after major updates. Removing an unused integration can meaningfully improve privacy measures.
Device Security Matters as Much as Cloud Security
A stolen phone, compromised companion app or outdated wearable can expose information regardless of how carefully a cloud model is protected. Any AI glasses privacy assessment should therefore include device pairing, software updates and account recovery.
The NIST consumer IoT cybersecurity profile describes capabilities commonly needed to protect connected consumer products. Its guidance is a starting point for evaluating wearables, not a certification of any specific pair of glasses.
Manufacturers should provide a supported update mechanism, clear security information and ways to manage device access. NIST also outlined foundational cybersecurity activities for IoT manufacturers in April 2026. Buyers should consider whether a lost device can be disconnected from an account and how locally stored recordings are protected.
Wearables may spend long periods in public environments, where network conditions and physical security are unpredictable. A secure architecture assumes some connections will fail and avoids exposing sensitive information through unsafe fallback behavior.
Camera-Free Glasses Change the Risk, Not the Entire Problem
Removing a camera eliminates the device’s ability to take ordinary photos and video through that component. It also makes certain visual AI features unavailable. Audio-only glasses can still use microphones, wireless connections and services that process personal information.
That is why a camera-free design should not be described as privacy risk-free. Voice recognition, call handling and connected assistants can involve other people or reveal sensitive details about the wearer.
TechAmerica.ai has covered the development of camera-free AI eyewear. The broader comparison shows that privacy depends on the sensors actually present and how their outputs are handled, rather than the presence of an AI label alone.
For some users, the absence of a camera may matter most. Others may care more about offline commands, retention settings or whether their everyday workplace permits wearable microphones.
How to Evaluate AI Glasses Privacy Before Using Them
Start with a practical assessment by identifying the exact model and software version. Check whether the glasses have a camera, which features require remote processing, and what indicators appear during photo, video, and visual AI requests.
Next, examine the companion app. Review permissions, stored media, voice-history controls, deletion procedures, and how the device uses information to improve AI systems. Privacy settings may differ by region, account or feature availability.
Test ordinary situations without involving unwitting bystanders. Try an offline command, inspect how a recording is imported and check whether the device clearly communicates a change in capture mode. Do not attempt to turn off safety indicators to conduct these checks.
For workplace deployments, add an assessment of approved locations, employee notice, support procedures and data-protection responsibilities. A device that suits personal use may be inappropriate for a meeting involving confidential clients.
What Trustworthy Wearable AI Should Make Clear
AI glasses privacy is not a single switch. It depends on the difference between gallery recording and temporary AI input, between local and remote processing, and between the wearer’s controls and a bystander’s lack of them.
Better chips and confidential cloud systems can reduce certain technical risks. Clear indicators, narrow permissions and meaningful deletion controls can address others. None removes the need to explain what information is collected or to respect people who did not choose to use the device.
The most useful standard for consumers is understandable behavior. They should be able to tell when sensors are active, what an AI request sends beyond the glasses and how to stop or erase permitted records. For manufacturers, that clarity is part of building wearable technology people can use responsibly.