




ClickFix Attacks Trick Mac and Windows Users Into Installing Malware
ClickFix attacks are tricking Mac and Windows users into running malicious terminal commands, with a recent campaign using compromised HBO Max ads on Reddit.
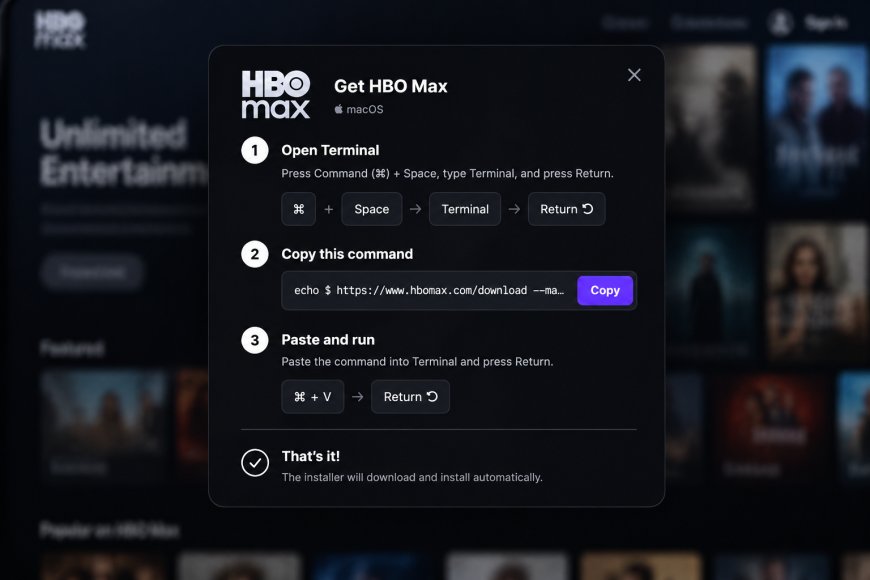
A fast-growing cyberattack technique known as ClickFix is tricking Mac and Windows users into installing information-stealing malware themselves, often after they encounter what appears to be an ordinary CAPTCHA or security check.
The attack typically begins on a fake website or a compromised legitimate site. Victims are shown instructions to copy and paste text into Windows Command Prompt, PowerShell or the macOS Terminal. Running the command can install malware that steals passwords, active account sessions, and cryptocurrency wallet data.
Because victims manually execute commands through operating-system tools, ClickFix campaigns can sometimes bypass defences that would otherwise block a conventional malicious download.
Compromised HBO Max account used for malicious Reddit ads
A recent campaign used advertisements posted through a compromised HBO Max account on Reddit, according to researchers at Hudson Rock. The ads directed users to a page designed to resemble HBO Max before presenting the ClickFix lure.
The campaign was also discussed in Reddit’s cybersecurity community, where users highlighted the malicious advertisements and their connection to information-stealing malware.
Reddit said an HBO Max account authorised to advertise on the platform had been compromised and used to distribute malicious links. The company said it locked the account and removed the advertisements but did not disclose how many users viewed or clicked them.
It remains unclear how many people were infected. Warner Bros. Discovery, which owns HBO, did not respond to a request for comment, according to the source report.
Why ClickFix attacks are difficult to stop
The technique relies heavily on social engineering rather than exploiting a software vulnerability. Users are persuaded to perform the critical step themselves by running commands they may not understand.
Security researcher Kevin Beaumont has noted that organisations managing Windows fleets can restrict access to command-line tools across managed systems, reducing opportunities for this type of attack.
The threat is also spreading beyond Windows. Ars Technica reported that ClickFix campaigns are increasingly targeting both PCs and Macs as attackers refine the technique and distribute it through broader advertising and web campaigns.
Mac users can also consider security tools designed to detect persistent software installations. One example is BlockBlock, which monitors attempts by software to establish persistence on macOS.
The simplest defence remains avoiding instructions from unfamiliar websites that ask users to paste commands into Terminal, PowerShell or Command Prompt. Legitimate CAPTCHA checks and routine website verification processes generally do not require visitors to execute operating-system commands.
What's Your Reaction?
 Like
0
 Dislike
0
 Love
0
 Funny
0
 Angry
0
 Sad
0
 Wow
0